AIOps DevOps Services.
Built so your pager stays quiet, not just your dashboard looking busy.
Triotech Systems delivers AIOps DevOps services that turn 2am pages into background noise ML telemetry pipelines, automated runbooks, and self-healing infrastructure that intercept chaotic system anomalies before they ever wake an engineer, embedded into your existing stack, not another dashboard nobody actually watches at 3am.
What are AIOps DevOps services?
The plain version
Machine learning and automation applied to the operational side of running software the monitoring, the incident response, the 3am judgment calls about whether something's actually broken or just noisy. Traditional DevOps handles building and shipping code reliably. AIOps watches what happens after it ships, and increasingly, fixes what it finds without waiting for a human to notice first.
Clear lines of ownership.
What the platform gives you, what we take on, and what you get at the end.
ML telemetry pipelines
ML telemetry pipelines that learn what normal actually looks like for your systems, instead of static thresholds someone set two years ago.
Automated runbooks & self-healing
Automated runbooks and self-healing infrastructure built around the failure patterns your systems actually produce, refined as new ones show up.
A quieter pager, measurably
40–60% reductions in mean time to resolution not a marginal improvement, but the difference between a bad night and a normal one.
Here's what's actually in scope.
What's included
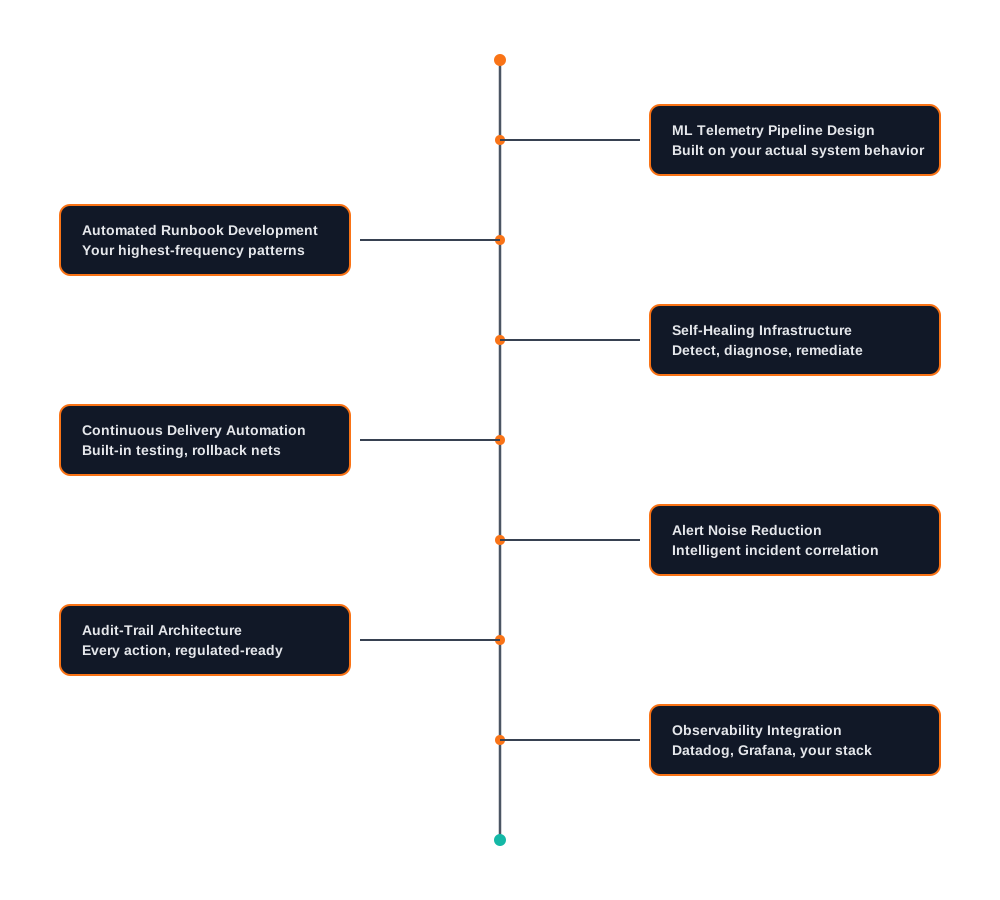
- ML telemetry pipeline designBuilt on your actual system behavior.
- Automated runbook developmentFor your highest-frequency incident patterns.
- Self-healing infrastructure automated detectionDiagnosis, and remediation.
- Continuous delivery automationWith built-in testing and rollback safety nets.
- Alert noise reduction and intelligent incident correlation
- Audit-trail architecture for every automated actionBuilt for regulated industries.
- Integration with your existing observability and incident management tools
- ML telemetry pipeline designBuilt on your actual system behavior.
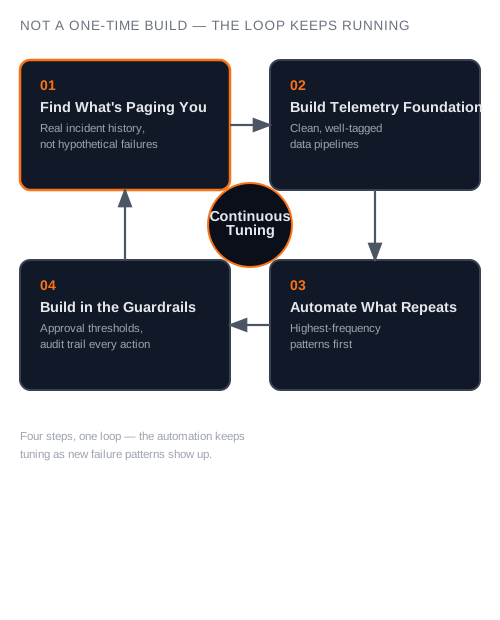
Four steps, one goal: software your agents actually trust.
INCIDENT REVIEW → SELF-HEALING, AUDITABLE PLATFORM ONGOING →
Find out what's actually paging you
A review of your incident history — not hypothetical failure modes, the real ones that have already eaten someone's evening more than once.
Build the telemetry foundation properly
Clean, well-tagged data pipelines, because self-healing automation is only as good as the data it's reasoning over — bad telemetry in, bad decisions out.
Automate the patterns that repeat, first
Not everything at once the incidents that show up often enough to be worth a runbook, starting with whatever's costing your team the most sleep.
Build in the guardrails from day one
Approval thresholds, rollback policies, and audit trails for every automated action, especially critical for regulated DevOps for fintech work.
A track record auditors sign off on
Numbers matter more than promises here.
Built from everything else we run.
Why choose us
Running production since 2020
Running DevOps and infrastructure for fintech, healthcare, e-commerce, and crypto clients since 2020 — AIOps is where it all compounds.
We're honest about the failure rate
Nearly a third of AIOps rollouts fail industry-wide, usually from scope moving faster than quality data we'd rather tell you upfront.
Built for mid-market, not enterprise
Most AIOps case studies are BT Group and HCL-scale. We build for teams closer to your actual size, resource-conscious, not enterprise.
Compliance discipline, built in from the start
The same discipline that gets a client to a 7-month SOC 2 timeline is what makes an automated runbook trustworthy enough to run unattended.
Continuous delivery, without cutting corners
Faster deployment pipelines with the testing and rollback safety nets that mean fast and reckless never end up being the same thing.
We can start with just the alert fatigue problem
If your team is already drowning in alerts, we can start there without needing to sell you a whole platform transformation up front.
Why choose Triotech?
One team, six disciplines
AIOps, Cloud & FinOps, DevSecOps, Data & MLOps, AI Agents & QA, and product engineering.
Certified security leadership
CISSP, CSSLP, and DevSecOps-certified leadership sets the technical bar for every engagement, not just the sales conversation.
Multi-vertical experience
Engagements across finance, healthcare, and other regulated industries, where compliance and uptime requirements are non-negotiable.
Toronto-based since 2020
An engineering studio with a Toronto base, direct technical leadership, and a global engineering bench supporting clients across time zones.
Agile, CI/CD-driven delivery
Solutions shipped through automated development workflows and continuous integration/deployment, so releases stay fast without skipping review.
This work, in production.
Real engagements with numbers attached.
All case studiesNo flat number. A scoped proposal instead.
How it works
There's no flat number that would mean anything here — automating three or four key incident patterns is a very different engagement from a full self-healing build across a complex multi-cloud environment. We'll start with a look at your incident history and telemetry setup, and come back with a scoped proposal so you know the real cost and timeline before committing to anything.
Questions about AIOps & DevOps.
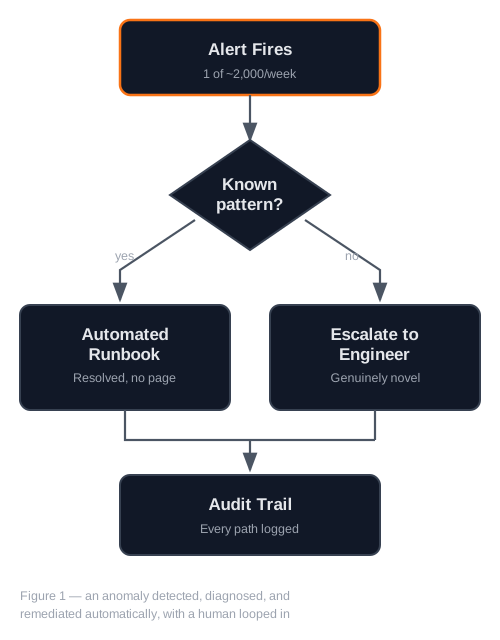
Regular DevOps automation handles building and shipping code reliably CI/CD pipelines, deployment scripts. AIOps adds machine learning to the operational side: watching telemetry, detecting anomalies, and increasingly, resolving known issues automatically instead of just alerting a human to go look.
No, and be skeptical of anyone claiming it will. It removes the repetitive, well-understood incident patterns from your team's plate — the kind of thing an experienced engineer could handle in their sleep. Novel, complex problems still need a human.
Yes, with the right guardrails built in from the start approval thresholds, rollback policies, and a full audit trail for every automated action. "The system fixed it" isn't sufficient in a regulated environment; you need to show exactly what it did and why.
Trying to automate everything at once, on messy telemetry data, without clear guardrails. Nearly a third of rollouts industry-wide don't deliver, almost always from scope moving faster than the underlying data quality and process discipline can support.
Book a working sessions
A security architect reviews your cloud, CI/CD and AI setup. Written report in five business days. Free.