E-Commerce. That Scales
Built so your busiest day goes fine, not viral for the wrong reason.
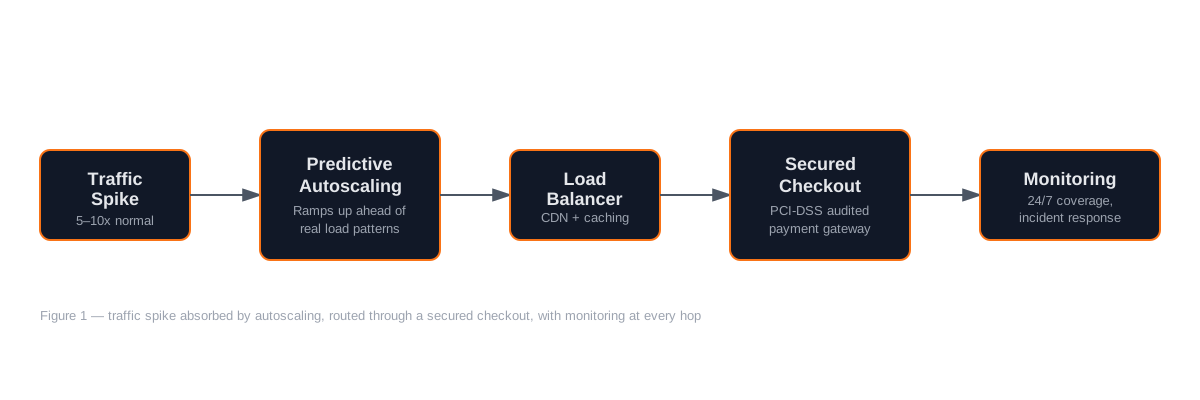
Triotech Systems builds and runs the infrastructure behind e-commerce platforms on Shopify, WooCommerce, Magento, or custom stacks — the autoscaling, payment security, and DevOps pipelines that keep checkout online when traffic hits five to ten times normal, not the version that only gets noticed the one day it fails.
What is E-Commerce Scalability Engineering?
The plain version
Making sure your store's infrastructure, payment processing, and the way your team ships code can all handle a lot more pressure than a normal Tuesday, without anyone finding out the hard way. It's not one-and-done what held up last November needs a second look before this one, because your traffic, integrations, and platform have all quietly changed since then.
Clear lines of ownership.
What the platform gives you, what we take on, and what you get at the end.
Predictive autoscaling
Predictive autoscaling infrastructure across your cloud stack, ramping up ahead of demand instead of reacting once the site's already straining.
Payment security & DevOps
Payment gateway security audited against PCI-DSS, database and query tuning, CI/CD pipelines your team can actually ship through during a sale.
A checkout that holds
Infrastructure that sustains five to ten times normal traffic without a hiccup, not a bigger hosting plan you're hoping holds on the day.
Here's what's actually in scope, concretely.
What's included
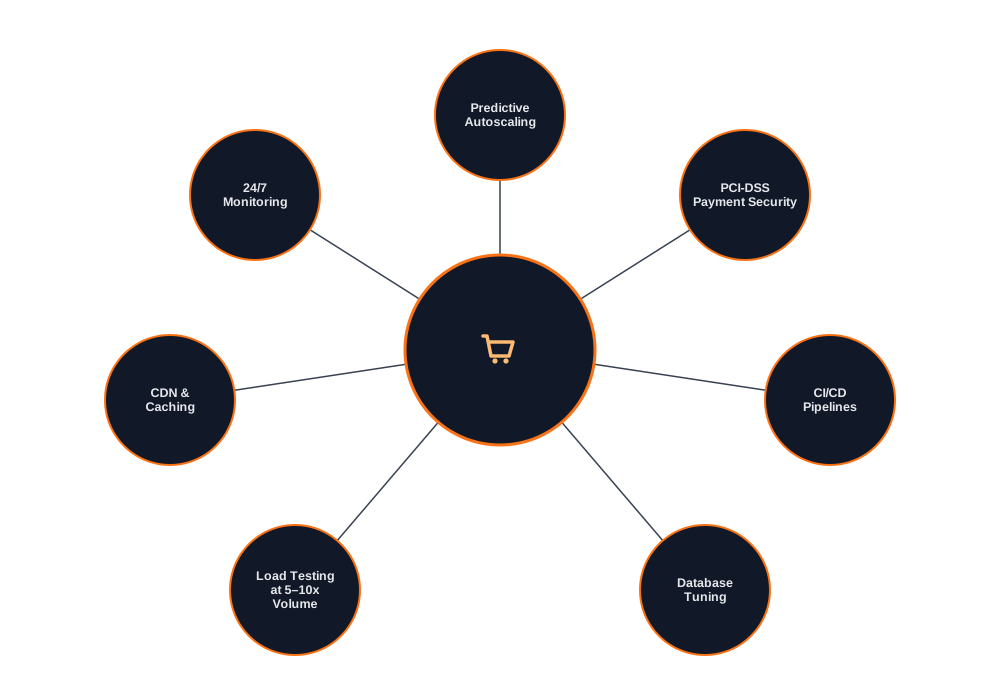
- Predictive autoscaling architecture across your cloud infrastructure
- Payment gateway integration securityAudited against PCI-DSS requirements.
- E-commerce DevOps pipeline setup CI/CDAutomated testing, deployment gates.
- Database and query performance tuningFor checkout and product-page load times.
- Load testing at realistic peak-traffic scenarios (5–10x normal volume)
- CDN and caching architectureFor product pages and static assets.
- Third-party API dependency review shippingTax, inventory, and payment integrations under load.
- Predictive autoscaling architecture across your cloud infrastructure (repeat, loop)
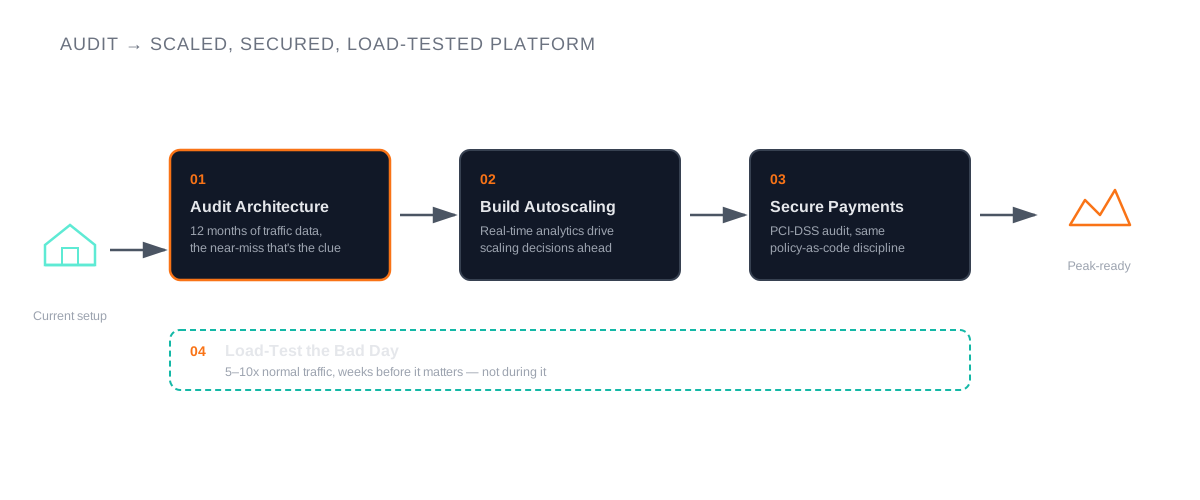
Four steps, one goal: your biggest day goes fine.
AUDIT → SCALED, SECURED, LOAD-TESTED PLATFORM
Audit your current architecture
Audited against PCI-DSS with the same policy-as-code discipline used for regulated fintech clients — because working and secure aren't the same claim.
Build infrastructure that scales ahead
Real-time analytics and historical patterns drive the scaling decisions, instead of a system that only reacts once you're already straining.
Learn your actual workflow
Twelve months of traffic data, your current setup, and the last time something almost went wrong that's usually the clue worth following.
Load-test the bad day on purpose
Five to ten times normal traffic hitting the same checkout endpoint at once, so we find what breaks somewhere quiet, weeks before it matters.
A track record auditors sign off on
Numbers matter more than promises here.
Built for what downtime actually costs.
Why Crypto teams choose us
Running production since 2020
Running production infrastructure for e-commerce brands since 2020, alongside our fintech, healthcare, and crypto compliance practice.
Any platform you're actually on
Shopify, WooCommerce, Magento, or fully custom we build around your real stack, not a template we're hoping fits.
Any platform you're actually on
Shopify, WooCommerce, Magento, or fully custom we build around your real stack, not a template we're hoping fits.
Watching during the hours that matter
24/7 monitoring with real coverage specifically around your planned high-traffic windows, not just whoever happens to be on call.
We already know your architecture
When something breaks live, that's the difference between a ten-minute fix and an hour reading your codebase for the first time.
A debrief after, not just a report before
A post-event debrief and capacity plan for whatever's coming next, so the same gap doesn't reopen at your next big moment.
Why choose Triotech?
One team, six disciplines
AIOps, Cloud & FinOps, DevSecOps, Data & MLOps, AI Agents & QA, and product engineering.
Certified security leadership
CISSP, CSSLP, and DevSecOps-certified leadership sets the technical bar for every engagement, not just the sales conversation.
Multi-vertical experience
Engagements across finance, healthcare, and other regulated industries, where compliance and uptime requirements are non-negotiable.
Toronto-based since 2020
An engineering studio with a Toronto base, direct technical leadership, and a global engineering bench supporting clients across time zones.
Agile, CI/CD-driven delivery
Solutions shipped through automated development workflows and continuous integration/deployment, so releases stay fast without skipping review.
This work, in production.
Real engagements with numbers attached.
All case studiesNo single number. A fixed-scope proposal instead.
How it works
There's no single number that would mean anything here a DTC brand gearing up for its first big sale needs something very different from a retailer running major promotions every other month. We'll get on a call, learn your platform and traffic history, and come back with a fixed-scope proposal covering the audit, the build, and the load testing, plus an optional retainer if you want us watching things ongoing.
Questions about E-Commerce Scalability.
Most scaling failures have nothing to do with horsepower. It's usually a database query nobody indexed, a connection pool that runs dry, or a checkout flow never tested past a handful of concurrent users. More servers just push the same failure a little further down the road.
Eight to twelve weeks, ideally. That gives us room to audit, make changes, and load-test before the event, not during it. Starting the week before means effectively testing in production — the most expensive way to learn where your limits are.
There's overlap, but PCI-DSS adds specific requirements around how cardholder data gets handled, tokenized, and logged that general security practices don't automatically cover. It needs its own build and its own audit.
Yes, and this happens often. We come in, figure out what actually failed, fix the real architecture problem, and load-test it properly before your next big moment, instead of everyone just hoping it doesn't happen again.
Book a working sessions
A security architect reviews your cloud, CI/CD and AI setup. Written report in five business days. Free.